Two engineers you trust give you opposite answers in the same meeting. One wants FreeRTOS on the existing microcontroller and says the product will ship in half the time. The other wants embedded Linux, argues the connectivity roadmap makes it inevitable, and says doing it later will cost more than doing it now. Both are right about something. Nobody in the room can put a number on the difference, and the decision gets deferred to the next meeting, where it will be no easier.
That decision is the one that quietly sets the cost, the schedule, and the maintenance burden of the entire product. It is made early, on incomplete information, by people who will not be the ones living with it in year four. Getting it right is less about knowing the options — most teams know them — and more about knowing which four or five facts about your own product actually decide it.
This article covers the ground between the idea and the shortlist: what embedded software development covers, how the stack choice is made, what the delivery process looks like step by step, where the work goes wrong, and what drives the number on the quote. If you already know how the software should be built and are working out who should build it, the top embedded software development companies roundup compares eleven firms against published, verifiable capability.
- The bare metal, RTOS and embedded Linux decision is driven by four inputs — worst-case timing, memory and power budget, concurrency and connectivity, and long-term maintenance headcount — and should be documented with its reasoning, because reversing it later is expensive.
- Firmware and embedded software are used interchangeably on small products and stop being interchangeable the moment there is an operating system in the middle.
- Hardware readiness, not estimation quality, is what moves embedded schedules; a first-spin board with live errata invalidates every plan built on top of it.
- Testing on target hardware is the load-bearing part of the process, because the defects that matter appear under thermal, electrical and timing stress that simulation does not reproduce.
- AI genuinely compresses the surrounding work — drivers scaffolding, test expansion, documentation — and does not compress the parts that need judgment: architecture, timing analysis, and reading a scope trace.
- Security and update capability moved from optional to structural, and the EU Cyber Resilience Act is the reason product teams are now scoping OTA and vulnerability handling from the start.
What Is Embedded Software?
Embedded software is software that runs on a device to make that device do its job, rather than on a general-purpose computer to run whatever the user opens. It lives on the processor inside the product — a microcontroller in a sensor, a system-on-chip in a vehicle head unit, a small applications processor in an industrial gateway — and it is written against that specific hardware, with a fixed memory budget and, usually, deadlines it must meet every cycle.
In practice the term covers a much wider range of activity than “writing code for a chip”. A single product can involve initializing hardware at power-on, writing drivers so the processor can talk to its sensors and radios, integrating or configuring an operating system, building the application logic, implementing a communication stack, and constructing a mechanism for updating all of it in the field years later. Those are different disciplines with different specialists behind them, which is why embedded systems software teams look different from application teams.
What makes writing software for embedded systems hard is that the constraints are physical and non-negotiable. An application server under load can be given more memory. A battery-powered sensor cannot, and neither can a control loop that has 200 microseconds to respond. Every design decision in embedded work is made against a ceiling somebody else set, and most of the interesting failures are timing failures that only appear when the hardware is warm, the bus is busy, or the battery is low.
Embedded Software vs Firmware
The distinction people ask about most is embedded software vs firmware, and the honest answer is that it depends on how big the product is.
Firmware is the layer closest to the metal: the bootloader, the low-level initialization that runs before anything else, and the code that drives peripherals directly. It typically lives in non-volatile memory on the device and is updated as a whole image rather than as separate components.
Embedded software is the umbrella term. It includes firmware and everything above it that still runs on the device — an RTOS or an embedded Linux system, middleware, the application logic, and any interface the user touches.
On a small microcontroller product, there is nothing above the firmware layer, so the two words describe the same thing, and arguing about them wastes time. The difference between firmware and embedded software starts to matter once a product has an operating system in the middle, because then you have components with separate release cycles, separate update mechanisms, and separate ownership — and a conversation about “updating the firmware” becomes genuinely ambiguous.
Embedded Software Examples Across Industries
The useful embedded software examples are the ones that show how differently the same discipline behaves under different constraints:
- Automotive. Engine and body control units running AUTOSAR-based software under functional safety requirements, alongside infotainment systems that are effectively Linux computers with a hard boot-time target.
- Medical devices. Infusion pumps, patient monitors, and diagnostic instruments, where the software lifecycle itself is regulated and every requirement must be traceable to a test.
- Industrial. PLCs, motor controllers, and machine safety systems, where a missed deadline is a physical event, not a dropped frame.
- Energy and utilities. Smart meters and charge points, where the constraint is a decade of field life on hardware that must stay secure and remotely updatable.
- Consumer. Wearables, appliances, and audio devices, where the binding constraints are unit cost, power draw, and manufacturing volume.
Why Embedded Software Development Is Harder Now
Two things changed at once, and they compound:
- Product value moved into the software. Hardware capability has converged across most categories: comparable silicon is available to everyone, and the difference between two competing devices is increasingly what the software does with it and how long the product keeps improving after purchase. That raises the ceiling on what embedded teams are asked to deliver — connectivity, remote diagnostics, on-device intelligence, feature updates to an installed base — on the same processors and the same power budgets as before.
- Security became a market-access requirement. Update capability and vulnerability handling used to be engineering preferences. Under the EU Cyber Resilience Act, there are conditions of sale: secure boot, image signing, a working over-the-air path, and a vulnerability process are now scoped at the start of a program rather than retrofitted by whoever has capacity in year two. The three dates that set the schedule, and what each obligation does to a firmware codebase, are set out in the Cyber Resilience Act requirements for firmware teams. Retrofitting them is possible, and it is consistently among the most expensive tasks a hardware team can be asked to do.
The compounding cost of standing still is straightforward arithmetic. A product shipped without a reliable update path is a fleet you cannot patch, and every unit sold only increases the problem. That does not make a rewrite the right answer — most products do not need one — but it does move update architecture from the “later” list to the “before first shipment” list.
Bare Metal, RTOS, or Embedded Linux: The Three Options
Ordered by degree of change and cost:
- Bare metal. No operating system. Your code runs in a main loop with interrupt handlers, and you control exactly what happens and when. Smallest footprint, tightest timing control, lowest overhead, and the highest cost of adding concurrency later.
- An RTOS — FreeRTOS, Zephyr, ThreadX, and others. A scheduler, tasks, and synchronization primitives on top of a microcontroller. You pay a modest memory and complexity cost and get structured concurrency, which is why this is the default choice for connected products with several things happening at once.
- Embedded Linux. A full operating system with a filesystem, a networking stack, package management, and a graphics stack, built for your board through a board support package and usually a Yocto- or Buildroot-based image. It needs an application processor and meaningful RAM, and it offers a large surface area to configure, secure, and maintain — in exchange for capabilities that would take years to build otherwise. Embedded Linux software development is also the option with the longest ramp, because the BSP must exist before application work can start.
Real products mix them. A vehicle instrument cluster may run embedded Linux for the display while a separate microcontroller runs safety-relevant functions bare metal, with a defined interface between them. An industrial gateway commonly pairs a Linux application processor with an RTOS-based real-time co-processor. The split is a design decision in its own right, and it is often a better approach than forcing a single stack to do both jobs.
How the Choice Is Actually Made
Four inputs decide it, and none of them is preference:
- Worst-case timing. Not average latency — the deadline you must never miss, and what happens physically if you do.
- Memory and power budget. How much RAM and flash the chosen part has, and what the energy budget permits an idle scheduler to consume.
- Concurrency and connectivity. How many independent things happen at once, and how rich the networking and update requirements are.
- Who maintains it. A three-person team maintaining a bare-metal codebase across four product variants in year five is a real cost, and it is the input most often left out of the decision.
Document the answer and the reasoning together. The decision is cheap to make and expensive to revisit, and in three years, the reasoning is what tells the next team whether the constraint that drove it still holds.
The Embedded Software Development Process, Step by Step
The sequence below is what a well-run embedded software development process looks like. Each step exists to buy down a specific risk, and skipping one moves that risk later, where it costs more.
1. Hardware and constraint assessment. Map the processor, the peripheral set, the timing requirements, the power envelope and the integration dependencies before any code is written. What this buys is that constraints surface in planning rather than mid-build, when changing course means changing hardware.
2. Architecture and stack decision. Choose bare metal, RTOS or Linux against the four inputs above, define the hardware abstraction boundaries, and decide the update and security architecture now rather than after the application works. Reviewed and documented, this is the artifact the whole build is measured against.
3. Board bring-up and BSP. Get the board to boot, initialize the clock tree and peripherals, and produce a board support package on which the rest of the software can be built. On a first-spin custom board, this step also finds the hardware errata, which is exactly what it is for.
4. Driver and firmware development. Peripheral drivers, the communication stack, and the application logic, built against the abstraction boundaries set in step two. On an automotive human-machine interface program we delivered in C++, QML and Qt over CAN, this was where multi-language support and a valet-mode security function were built as separable components rather than as features tangled into the interface — which is why adding the next one stayed cheap.
5. Verification on target hardware. Unit tests, hardware-in-the-loop validation, and boundary-condition analysis run in parallel with development rather than as a phase at the end. This is the step that decides whether the product works outside the lab, and it is the one most often compressed when a schedule slips.
6. Production transition and field support. Production firmware variants, device programming configuration, manufacturing test fixtures, and a defined post-deployment monitoring window. Products meet their real conditions after they ship, and the plan needs to survive that.

Challenges Worth Planning For in Embedded Systems Software Development
- Hardware readiness. Late boards, first-spin errata, and shared prototype hardware invalidate software schedules regardless of the quality of the estimates. Plan for staged hardware availability, get emulation or a development board in place early, and state the assumption explicitly so everyone can see when it breaks.
- Timing defects that only appear under load. Race conditions, priority inversion, and interrupt latency problems are frequently invisible in benign conditions and reproducible only when the board is warm and the bus is busy. Hardware-in-the-loop rigs and long-run soak tests are what find them; code review alone does not.
- Toolchain and build reproducibility. Embedded builds depend on specific compiler versions, linker scripts, and vendor SDKs, and a build that only works on one engineer’s machine is a liability that surfaces at the worst moment. Pin the toolchain, put it in CI, and treat the build environment as a deliverable.
- Certification scope discovered late. Requirements traceability, documented verification, and design history are not paperwork added at the end under IEC 62304 or ISO 26262 — they change how requirements and tests are managed from day one. Discovering this in month five is one of the most expensive discoveries available.
- The update path as an afterthought. Secure boot, image signing, rollback behavior, and what happens when an over-the-air update fails halfway are architecture, not features. Retrofitting them into a shipped fleet is possible, and it is never cheap.
- Knowledge that leaves with people. Embedded codebases are dense, hardware-specific, and frequently under-documented, and the original authors move on. Documented abstraction boundaries and a transferable build environment are what keep the product maintainable, which is why they belong in the statement of work.
Embedded Software Development Tools and Where AI Helps
The tool categories are stable, and the specific names matter less than having each category covered:
- Toolchains and IDEs — vendor and open toolchains, cross-compilers, and the vendor SDK for the chosen silicon family.
- Build systems — Yocto or Buildroot for Linux images, CMake and dependency management for firmware.
- Debug and trace — JTAG and SWD probes, on-target debuggers, logic analyzers and oscilloscopes. The last two are still where hard timing problems get solved.
- RTOS and middleware — the scheduler and the communication, storage and security components on top of it.
- Test infrastructure — unit test frameworks, hardware-in-the-loop rigs, static analysis, and CI runners with real boards attached.
- Security tooling — signing infrastructure, CVE monitoring against your dependency set, and SBOM generation.
AI has become genuinely useful across part of this list. In our own AI-enabled engineering model, agents generate driver and peripheral boilerplate, expand test coverage against boundary conditions, and keep documentation current alongside the code — work that is real, repetitive, and previously took weeks. On a manufacturing operations build delivered by an AI Pod, that model produced an MVP 63% faster with a 56% smaller delivery team than a traditional build of the same scope.
What it does not compress is the part that requires judgment. Architecture decisions, worst-case timing analysis, reading a scope trace to work out why a bus glitches on a warm board, and deciding whether a failure mode is acceptable are still engineering, and the output of an agent that has not been reviewed by someone who can do those things is plausible firmware, which is worse than obviously wrong firmware. The useful question about AI in embedded work is not whether a team uses it — most now do — but who is accountable for what it produces.
What Embedded Software Development Looks Like in Practice
Embedded work is judged on what happens after the first release, when the second and third features arrive and the boundaries drawn early either hold or start charging rent.
An automotive supplier needed HMI features shipped faster than its release train allowed. Hybrid and electric vehicle programs kept adding interface requirements — text-to-speech, valet mode, phone projection, end-of-line configuration — and each one was landing as a change to a tightly coupled interface, so each one cost more than the last. A five-engineer team working in C++, QML, Qt and Python over CAN, Wayland and CommonAPI rebuilt the features as separable components against clean boundaries. Feature deployment ran 2x faster, hands-free system usage rose 30%, and the interface shipped in 8 languages.
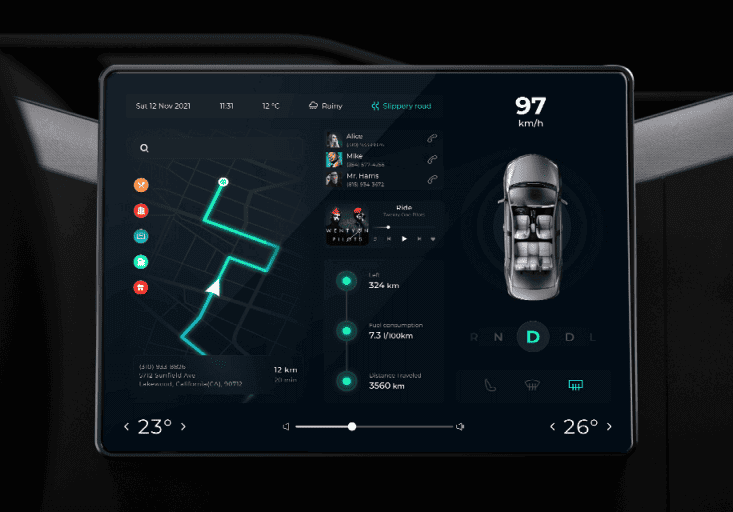
The win came from structure rather than cleverness. Rebuilt as separable components against clean boundaries, the features stopped competing with each other, and the deployment speed, the usage numbers and the localisation all followed from that. The boundaries settled early are what decide the cost of every change after them.
Trends in Embedded System Software Development
Memory-safe languages are entering production firmware. Rust has moved from argument to shipped code in automotive and industrial work, including migrations of time-critical components within existing AUTOSAR environments — automotive embedded software development is where memory-safety pressure landed first and where the tooling has matured to meet it. It is not replacing C, and mature C codebases rarely justify a rewrite — but for new safety-relevant components, the calculation has changed.
Intelligence is moving onto the device. Inference at the edge is now viable on parts that would not have supported it a few years ago, which shifts the design problem from model accuracy to power, memory, and thermal envelope. The constraint is the hardware, not the model, and scoping it as an IoT development question rather than a data science one produces better answers.
Software-defined products are pulling architecture toward updatability. Consolidating functions onto fewer, more capable processors, separating safety-critical from feature workloads, and designing for a decade of remote updates are becoming default assumptions rather than advanced practice — driven as much by regulation as by product strategy.
Conclusion
Most embedded programs are decided by three things settled early: the stack, the update architecture, and whether verification happens on real hardware throughout or only at the end. Get those right and the rest of the work is normal engineering. Get them wrong and no amount of delivery discipline recovers the schedule.
Once the approach is settled, the remaining question is who does the work — and that is a different comparison, made against published capability rather than against intent. The top embedded software development companies roundup ranks eleven firms across the three tiers that serve this market, with the criteria to match them to your own scale.