Lift-and-Shift Migration of a Patient Scheduling & Billing System to AWS

Up to $300K
in hardware refresh costs eliminated
99.9%+
system availability
Lift-and-Shift Migration of a Patient Scheduling & Billing System to AWS | Crunch-IS Case Study
A fast, low-risk cloud migration that reduced operational risk and improved availability for revenue-critical healthcare workflows — without disrupting clinical operations.
Industry:

Healthcare (Outpatient Clinics)

Location:

US

Team Size:

5

Duration:

10 weeks

Technologies
VMware vSphere
Windows Server (IIS)
Microsoft SQL Server
AWS
Amazon EC2
Amazon VPC
Site-to-Site VPN
AWS IAM
AWS KMS
AWS CloudTrail
Amazon CloudWatch
AWS Backup
Terraform
CI/CD
01

About the Client

The client is a small healthcare organization operating outpatient clinics in the US. Internal teams depend on a web application for patient scheduling, eligibility checks, and billing exports, which is tightly integrated with their EHR system.

The application was business-critical and any downtime directly affected clinic check-in processes and downstream billing operations.
Lift-and-Shift Migration of a Patient Scheduling & Billing System to AWS | Crunch-IS Case Study
02

Challenge

The client was running the application on an on-premises VMware environment that was becoming increasingly risky to operate.

Infrastructure components were approaching the end of life, unplanned downtime disrupted daily operations, and remote access for administrators and support teams was limited by VPN bottlenecks. Inconsistent patch management and auditability increased operational and compliance risks.

At the same time, the organization needed to move quickly. Revenue operations could not tolerate a long refactor or modernization project, so the team chose a lift-and-shift (rehost) approach (migrating first and deferring optimization) while maintaining HIPAA-aligned security controls.

03

Solution We Delivered

Crunch-IS executed a controlled lift-and-shift migration to AWS, prioritizing speed, stability, and minimal application changes.

Migration Scope and Target Environment

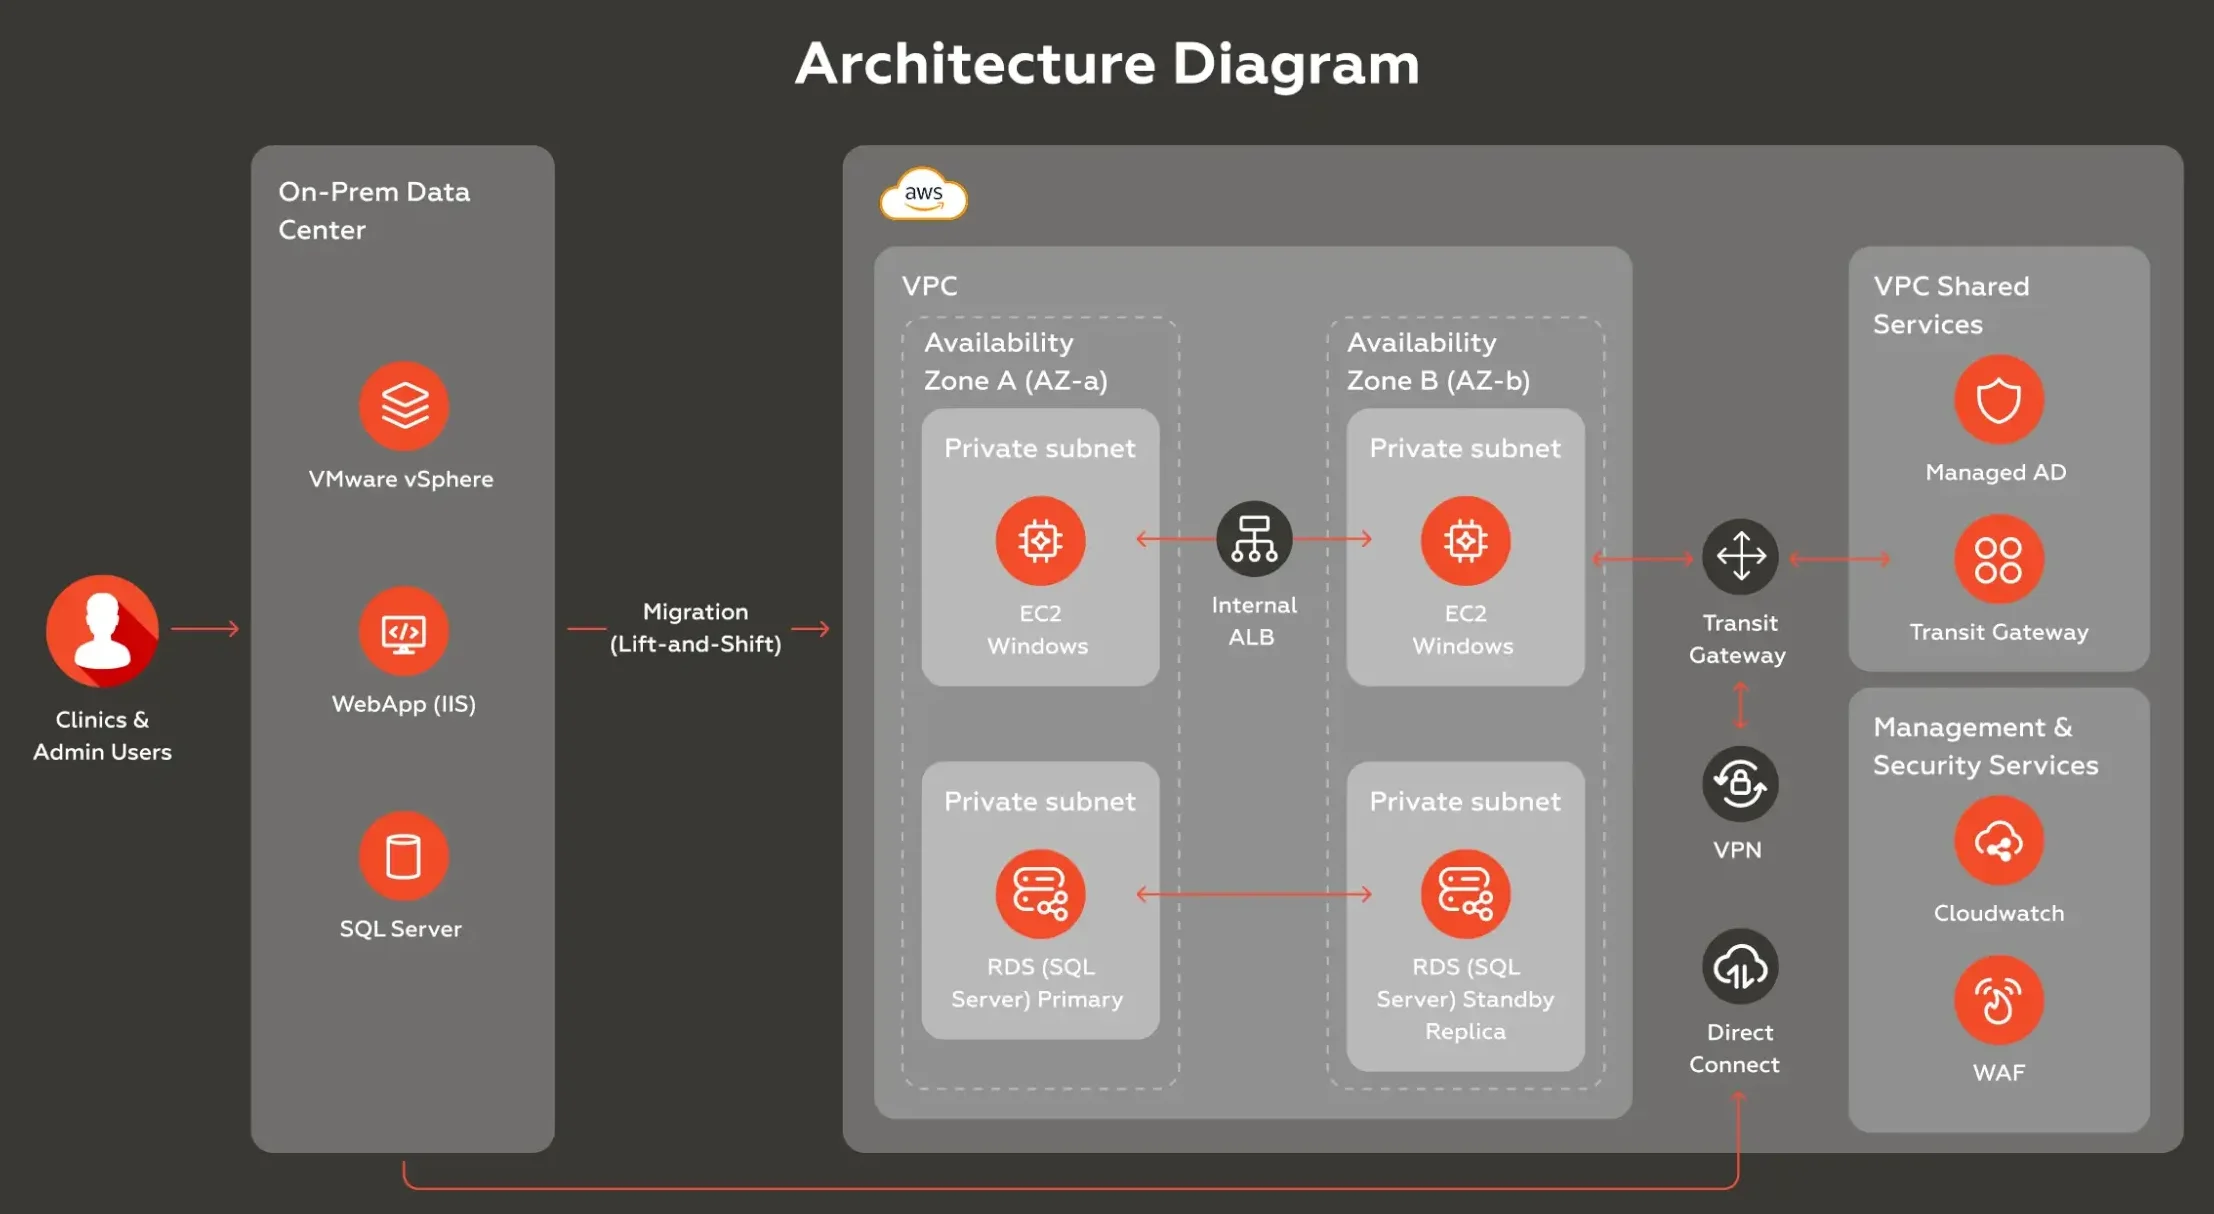
We designed a lightweight, production-ready AWS environment, establishing a dedicated VPC with clearly segmented public and private subnets. Web and database tiers were isolated within private networks, with controlled access granted to clinic staff and administrators.

Baseline EC2 configurations were prepared for Windows workloads, including a patching strategy, hardened AMIs, and a repeatable instance provisioning process.

To minimize risk and meet tight timelines, application refactoring, architectural redesign, and major EHR interface changes were intentionally deferred and kept out of scope for this phase.

Assessment and Migration Planning

Before execution, we mapped dependencies to identify EHR interfaces, scheduled export jobs, authentication flows, and supporting services.

The migration was structured into clear waves:

  • foundational networking, identity, and logging
  • web tier migration
  • database migration and synchronization
  • cutover, validation, and stabilization

Each wave included defined rollback steps and risk mitigation measures for performance, connectivity, and data consistency.

Data Migration Execution

Given the lift-and-shift constraint and the need to minimize application changes, we implemented a SQL Server migration approach compatible with the existing environment.

Data synchronization was handled using low-impact methods compatible with the client’s SQL Server edition, keeping the system operational until the final cutover. During migration, write activity was briefly paused, a final sync was completed, and connections were switched after validating key transactions and reports.

Minimal Application and Infrastructure Changes

Only essential configuration changes were introduced, such as database endpoints, internal URLs, and certificates.

Infrastructure was codified using Terraform to ensure repeatability and reduce manual intervention. A controlled deployment process for configuration updates replaced ad-hoc “RDP-and-click” changes, reducing operational risk.

Security and Compliance Controls

Security was integrated into the environment from the outset. Data was encrypted at rest and in transit, access was restricted using least-privilege IAM roles, and broad administrative access was eliminated.

Auditability was enhanced through centralized logging and CloudTrail. HIPAA-aligned operational controls were documented, including backup retention policies and incident response procedures.

Testing, Cutover, and Stabilization

Validation addressed both technical and operational readiness. Data reconciliation checks ensured consistency between billing and encounter data, while performance tests simulated clinic morning-rush scenarios.

The final cutover was completed during off-hours, with the on-prem environment maintained during the initial stabilization period. Post-migration support included monitoring dashboards, aligning patch cadence, and improving cost visibility to support future optimization.

Crunch-IS image case study
04

Client’s Results

As a result of the controlled lift-and-shift migration, the client achieved the following outcomes:

  • 99.9%+ system availability, reducing unplanned downtime by 70+ hours per year and protecting revenue-critical scheduling and billing operations.
  • Disaster recovery time was reduced from hours to minutes, with RTO (Recovery Time Objective) reduced from 4 to 8 hours to under 15 minutes and RPO (Recovery Point Objective) reduced from 24 hours to under 15 minutes, significantly lowering data loss and revenue interruption risk.
  • $150K–$300K in capital expenditure avoided by eliminating on-prem hardware refresh and licensing costs, allowing funds to be redirected toward patient care and operational priorities.
  • 50% reduction in infrastructure-related support tickets, freeing IT staff to focus on higher-value initiatives instead of manual maintenance.
  • Faster security and operational changes, with infrastructure updates moving from days to hours through Infrastructure-as-Code and automated deployments.
  • Stronger auditability and compliance readiness, reducing compliance audit preparation from weeks to days through centralized logging and automated evidence collection.

Have a Question? Let’s Get in Touch!

Tell us what you’re building or where you’re stuck. We work with engineering and product teams on custom software, AI & ML, cloud infrastructure, DevOps, and UI/UX — from early scoping to long-term delivery. One conversation is usually enough to know whether we’re the right fit.

Email: [email protected]

    I have read and accepted the Terms of Use and Privacy Policy *

    We and our partners use technology such as cookies on our site to personalize content and ads, provide social media features, and analyze our traffic. Click “Accept” to consent to the use of this technology across the web.

    Decline