
Don't see yours? Start with a conversation.
Talk to an AI expertCrunch-IS in numbers
- 170+
- experts
- 120+
- delivered projects
- 40+
- active customers
- 6+
- locations
- 8+
- years of experience

Home / Cloud Cybersecurity Assessment
Cloud Cybersecurity Assessment
Know your cloud’s current state, uncover risks early, and strengthen security before weaknesses are exploited.
Crunch-IS Cloud Cybersecurity Assessment examines how your AWS, Azure, Google Cloud, or Oracle environment is actually configured. We identify what’s exposed, explain what it means in business terms, and give you a concrete plan to fix it.

Challenges You Face

Permission Sprawl
As organizations grow, access accumulates. Over time, identities and permissions become scattered across the environment — and no one has a complete picture of who can do what.

Reactive Security Posture
Security work is triggered by incidents, audit findings, or compliance deadlines. The gaps were there before the incident; they just weren’t visible.

Fragmented Visibility
Multi-account and hybrid environments managed by different teams produce inconsistent monitoring coverage. Some workloads are watched closely. Others are running with alerts turned off or logs going nowhere.

Configuration Drift
Cloud environments are secure at deployment and degrade over time. Small changes accumulate — a security group rule loosened here, an encryption setting changed there. Drift is gradual, hard to track manually, and rarely caught until an audit or an incident.
Cloud Cybersecurity Assessment Benefits

Misconfiguration, permission gaps, and unmonitored workloads are identified, while remediation remains straightforward.

Requirements under SOC 2, ISO 27001, GDPR, HIPAA, and PCI DSS are mapped to specific controls in your environment.

The assessment produces a prioritized remediation roadmap. Security gaps are addressed in order of actual risk, and the foundation scales with your infrastructure.

Defined ownership of security controls means your teams know who is responsible for what. Incidents get handled faster, and audit responses stop being scrambled.
Want to know where your cloud security actually stands?
How We Help

Identity and Access Assessment
We analyze user roles, service accounts, authentication methods, and privilege boundaries across your cloud environment. The focus is on whether access is controlled and intentional. Overprivileged accounts, inactive identities, and weak authentication configurations are documented with specific remediation steps.

Network Security Assessment
We review segmentation, firewall rules, public endpoints, VPN configurations, and inter-service traffic patterns. Exposed services, overly permissive security group rules, and missing network controls are identified and prioritized by exploitability.

Data Protection Assessment
We evaluate encryption standards at rest and in transit, key management practices, backup strategy, and storage lifecycle policies. Sensitive data sitting in unencrypted storage, improperly scoped buckets, or missing backup coverage is flagged — along with what needs to change and why.

Logging, Monitoring, and Incident Readiness Assessment
We evaluate what activity is logged, how alerts are configured, and whether incident response procedures are defined and tested. A cloud environment without adequate logging fails silently. We map the gaps between what’s happening in your environment and what your team can actually detect.

Risk Prioritization and Remediation Planning
Not every finding poses the same threat. We rank each issue by severity and operational impact, producing a remediation plan that tells you where to focus first — and why. The output is actionable by your team without further interpretation.
Our Capabilities
Multi-Cloud Security Assessment
Assessment coverage across AWS, Azure, Google Cloud, and Oracle Cloud — including hybrid and multi-account environments where visibility gaps are most common.
IAM and Privilege Analysis
Role-based access control review, service account auditing, authentication policy evaluation, and privilege boundary mapping across cloud identities and federated systems.
Cloud Security Configuration Review
Platform-native security control evaluation against CIS Benchmarks and provider-specific security frameworks — with findings tied to your actual environment configuration.
Compliance Control Mapping
Requirements under SOC 2, ISO 27001, GDPR, HIPAA, and PCI DSS mapped to specific controls in your cloud environment — with gaps documented and remediation steps prioritized.
Threat Modeling for Cloud Architectures
Systematic identification of attack paths specific to your architecture — covering lateral movement risks, data exfiltration vectors, and misconfigurations that create exploitable entry points.
Remediation Roadmap Development
A prioritized, phased plan with effort estimates and ownership assignments — built so your team can implement findings without needing us in the room to interpret them.
What You Get

Built on Real Configuration
Every finding comes from direct technical analysis of your environment — how it’s actually configured.

No Security Theater
We focus on what genuinely affects your operational exposure. Not every finding requires emergency action, and we make that clear.

Business and Technical Clarity
Each risk is explained at both levels: what it means technically, and what it means for the business. Leadership and engineering teams work from the same report.

Engineers Who Execute What They Find
The engineers who run the assessment are the same engineers available to implement the remediations.
What Our Clients Say About Us
They come up with lots of scalable and best-practice ideas that enable us to achieve what we have right now.
Crunch-IS was great at leading us on what good should look like and bringing our ideas to life for evaluation and review.

Crunch-IS impressed me with is the quality of developers. It is simply much better than in any other company we’ve tried working with.

We are impressed with their performance, how they are engaged with product development, and how they care about the product.

It’s been a very enjoyable experience. All has been fantastic about communicating, and working.

Our partnership with Crunch-IS has been an invaluable resource as we’ve scaled.

What I found in Crunch-IS was the technical competency, ability to think outside the box, and very good English.

They have a large impact on the whole architecture we ended up with. Overall, I’ve been pleased and impressed with everything Crunch-IS did for us.

Crunch-IS impressed us with their technical excellence and the sheer ‘meeting of minds and cultures’ and open, honest exchanges. This was not a decision we took lightly, and 5 months into the engagement we continue to be really impressed with how Crunch-IS approach the collaboration, and we’re delighted with the calibre of the team we have working with us.

Working with Crunch-IS was easy. They were patient with us as we worked through the contract questions and patient again as we were getting our billing set up. The design work was elegant and the developer delivered the app we had contracted for on time and good quality.

The team at Crunch-IS was very nice to work with. They worked diligently and were very professional. When questions or technical problems arose, they answered them quickly and were always ready and kind about helping us.

Crunch-IS developer helped us deliver an important feature for our project much faster than expected.

Crunch-IS facilitated a seamless, collaborative effort throughout the project. The team maintained open lines of communication, kept detailed records of task assignments, and adhered to project timelines. Their expertise regarding both design and development sets the company apart.

Crunch-IS provides ongoing development support that meets project requirements as needed. Despite their offshore location, they are easy to work with and accessible through communication channels

The best vendor we could possibly find. Crunch-IS blends practical development with innovative design principals. Internal and external feedback to app development has been positive. They complete project milestones by the planned schedule and deliver within budget. The team’s responsive and willing to engage in productive dialogue.

Crunch-IS exceeded my expectations. I appreciated the developers’ resourcefulness in the face of constraints and complex requirements. The company able to deliver and complete the project successfully.

The project has gone smoothly so far. Crunch-IS has an exceptional work ethic. Consequentially, they’ve been able to tackle every challenge that comes their way. They manage day-to-day work on their own well but also communicate with us regularly to make sure we’re on the same page.

The app Crunch-IS worked on is clean, streamlined, and functions as intended. Crunch-IS goes above and beyond to ensure that both teams are in tune. The passionate team crafts an enjoyable experience through their positive demeanor and effective project management skills. The team was very friendly, and working with them was a pleasure.

Why Crunch-IS

Assessed Against
Reality
We evaluate your cloud environment as it’s configured today. Configuration drift, informal changes, and undocumented permissions are exactly what we look for.

Cloud and Security Engineering in One Team
Our team combines cloud infrastructure engineering with security expertise. We understand how cloud environments are built and how they fail — which means findings are grounded in operational reality.

Multi-Cloud Without Platform Bias
We work across AWS, Azure, Google Cloud, and Oracle Cloud. Recommendations follow your architecture and compliance requirements.
Cloud Cybersecurity Assessment FAQ
What is a Cloud Cybersecurity Assessment?
A Cloud Cybersecurity Assessment is a structured technical review of how your cloud environment is configured from a security standpoint. It examines identity and access management, network segmentation, data protection, logging coverage, and compliance control gaps — and produces a prioritized remediation plan. The goal is to find what’s exposed before it’s exploited, not after.
How is Cloud Cybersecurity Assessment different from ongoing cloud security services?
Technically, ongoing cloud services focus more on monitoring and response, while Cloud Cybersecurity Assessment involves an evaluation that identifies weaknesses and improvement areas before they become real problems.
How long does a Cloud Cybersecurity Assessment take?
Typically two to five weeks, depending on the size of the environment, the number of accounts or providers involved, and the complexity of compliance requirements. We scope the engagement accurately at the start — you’ll know the timeline before work begins.
If my cloud provider is secure, why do I still need an assessment?
Cloud providers must secure the infrastructure they operate and are responsible for how your workloads, identities, and data are configured. Most cloud issues arise from misconfiguration, and an assessment makes sure your environment is set up correctly and safely.
Can you help implement the findings after the assessment?
Yes. The engineers who conducted the assessment are available to implement remediations. There’s no separate implementation team. The people who found the issues fix them.
Crunch-IS Success Stories
A fast, low-risk cloud migration that reduced operational risk and improved availability...
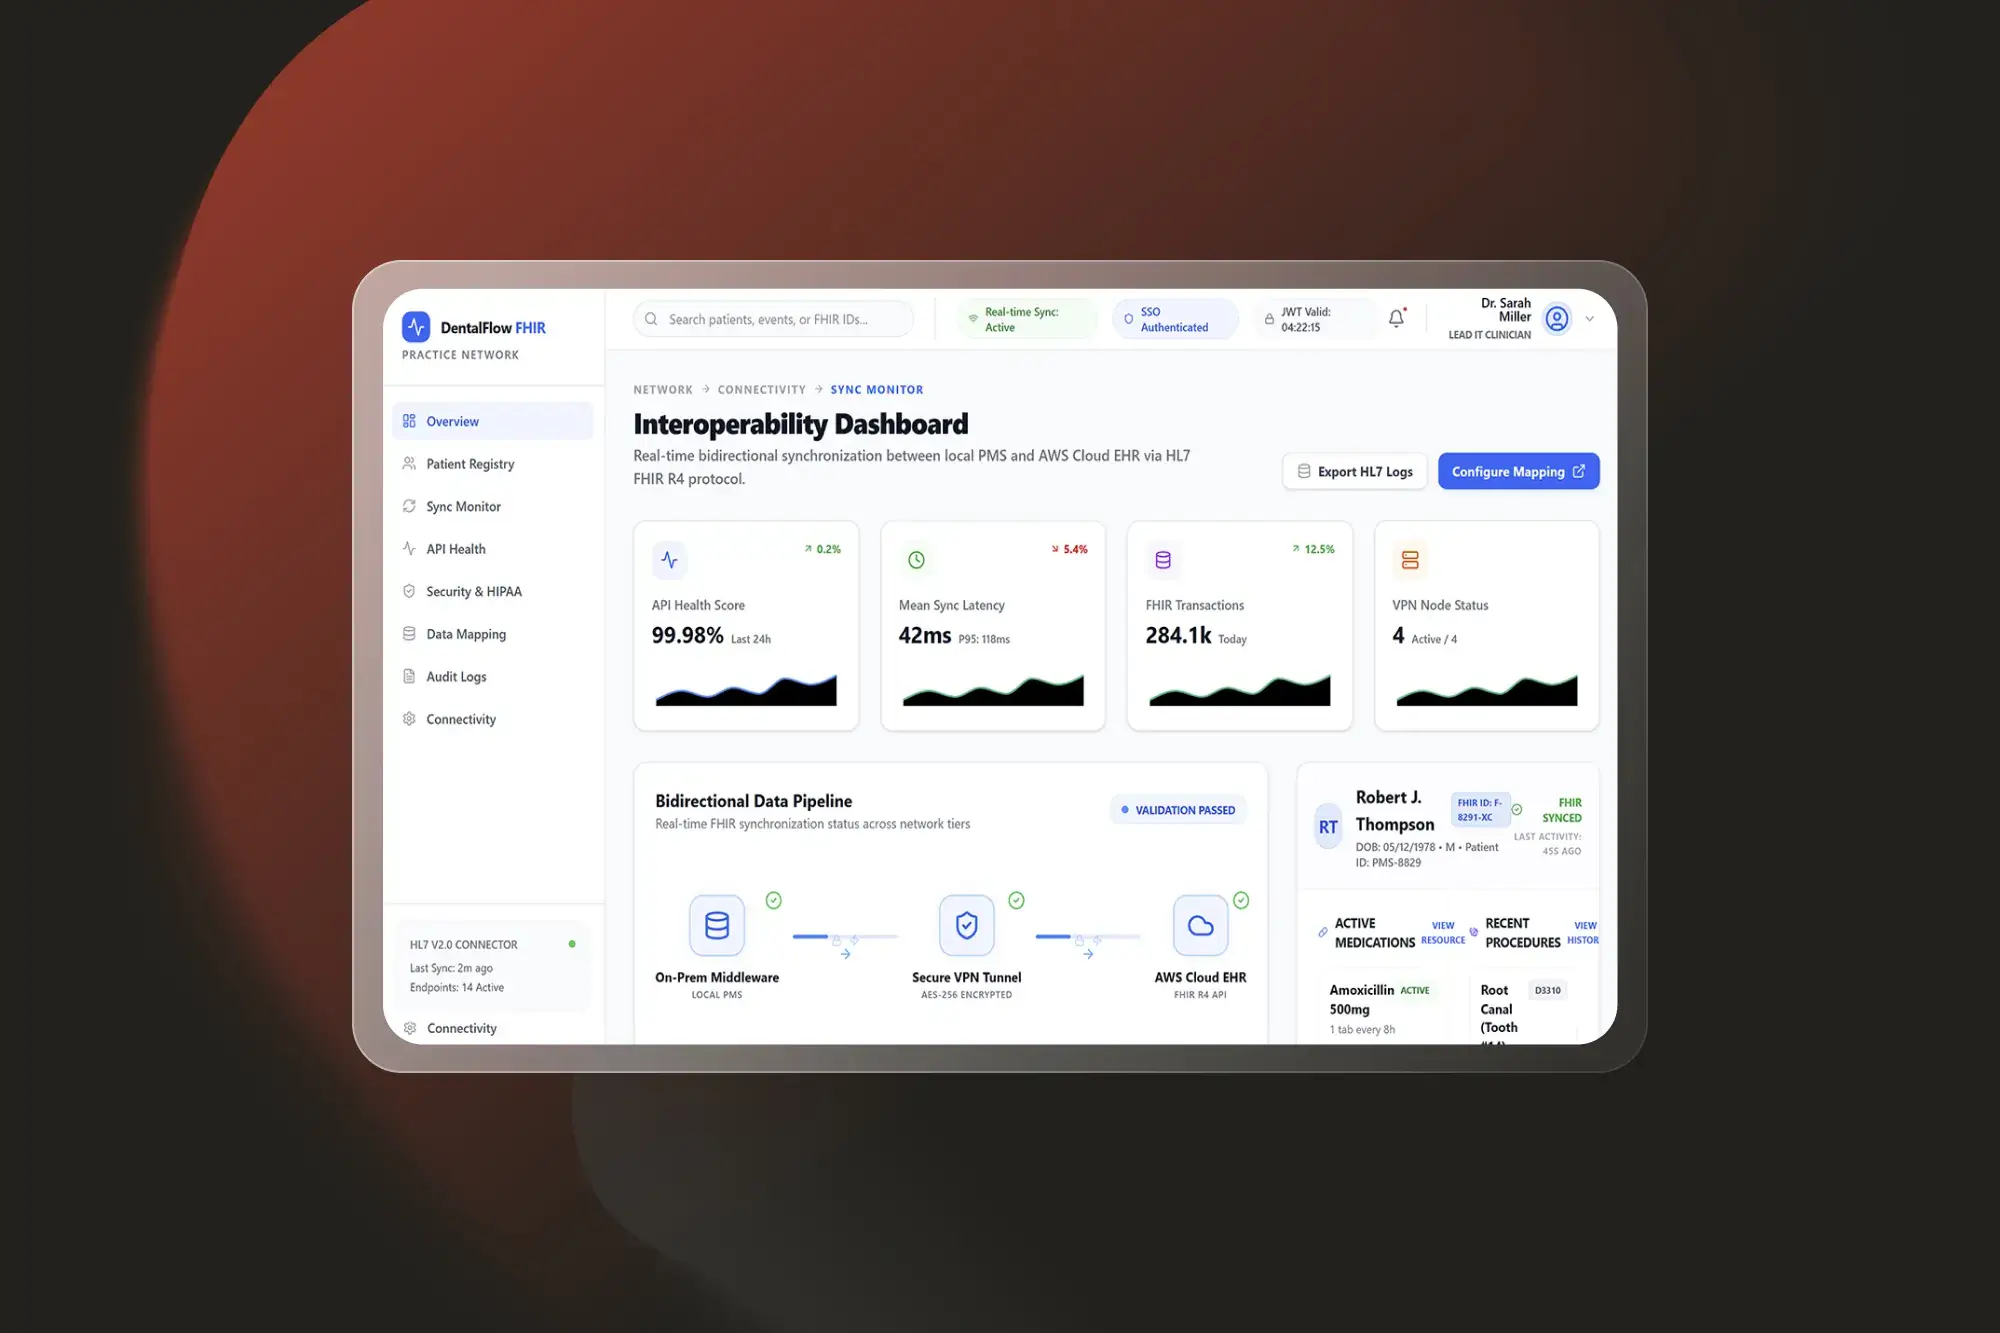
We delivered a standards-based HL7 FHIR interoperability solution for a dental practice...
A data-driven SaaS healthcare platform that optimizes patient management, financial tracking, and...
Stay Up-to-date with the Latest Trends and Innovations
Tell Us What You’re Building
Send an outline, a spec, or three sentences about where the system has stopped. One conversation is usually enough to know whether we’re the right fit.
Custom software, AI & ML, data and analytics, cloud, and security — from early scoping to long-term delivery.
- 170+ experts
- 120+ delivered projects
- 97% fully satisfied


